
Critical incidents often happen on private property, placing large enterprise organizations at the center of real-time response. Retailers, financial institutions, and other compliance-driven enterprises must share intelligence quickly while maintaining strict cybersecurity, privacy, and governance standards.
The challenge is not whether to share intelligence. It is how to share it without expanding system exposure risk. That requires incident response technology that improves situational awareness, preserves organizational control, and supports business collaboration with law enforcement without granting ongoing access to internal systems.
Key Takeaways
- Enterprise organizations need to balance intelligence sharing with organizational control.
- Persistent external access can increase cybersecurity, privacy, and governance risk.
- Controlled intelligence sharing supports collaboration with law enforcement without exposing internal systems.
- A governed, event-based approach strengthens incident response while maintaining enterprise oversight.
Governance and Compliance in Enterprise Security
Large enterprise organizations operate under layered cybersecurity frameworks, privacy laws, and internal governance policies. Any decision involving system access or external collaboration must align with documented risk management standards and audit requirements.
Sharing real-time intelligence with outside partners is not simply an operational decision. It is a risk management decision. Granting external access to cameras or security platforms can introduce new attack surfaces, expand monitoring obligations, and complicate compliance reviews.
In these environments, caution reflects discipline, not hesitation. Any intelligence-sharing model must strengthen response capabilities without altering the organization’s risk profile. For enterprise security teams, maintaining organizational control is essential to balancing effective incident response with cybersecurity, privacy, and governance requirements.
Why Persistent Access Can Increase Enterprise Risk
Traditional access models are built on persistent connectivity. External stakeholders are granted ongoing access to cameras or video management systems in the name of operational efficiency.
While convenient, this structure expands the enterprise attack surface and introduces continuous governance obligations. Persistent access requires monitoring, documentation, and periodic review to remain aligned with compliance standards. Over time, what begins as a response enhancement can evolve into sustained risk exposure.
Organizations are often presented with a false choice: restrict collaboration to protect systems, or expand access to improve response. Neither option reflects modern enterprise risk management. Effective intelligence sharing should enhance response without compromising control.
Maintaining organizational control does not mean limiting collaboration. It means ensuring that verified intelligence is shared intentionally, securely, and only when it supports an active incident.
Privacy by Design as a Strategic Advantage
In enterprise security environments, privacy safeguards must be embedded into the design of any intelligence-sharing model. Controlled frameworks prioritize situational context over broad system access, ensuring that only incident-relevant information is distributed.
Access should be time-bound, acknowledgment-based, and fully auditable. Every sharing decision is documented, creating clear oversight aligned with internal policy and regulatory expectations.
By limiting exposure to what is necessary and appropriate for each verified incident, organizations strengthen trust with both internal stakeholders and public safety partners. Privacy is not a barrier to response. When designed correctly, it becomes a strategic advantage.
Strengthening Response Through Controlled Intelligence Sharing
Putting privacy-by-design principles into practice requires a governed approach to intelligence sharing. Instead of opening internal systems, enterprises curate relevant information and distribute it through controlled pathways.
DirectToDispatch™ applies this approach by enabling organizations to share verified, incident-specific intelligence through governed access.
For each verified incident, enterprises establish defined parameters, including:
- What intelligence is shared
- Who receives access
- How long visibility remains available
- Whether distribution is internal, external, or both
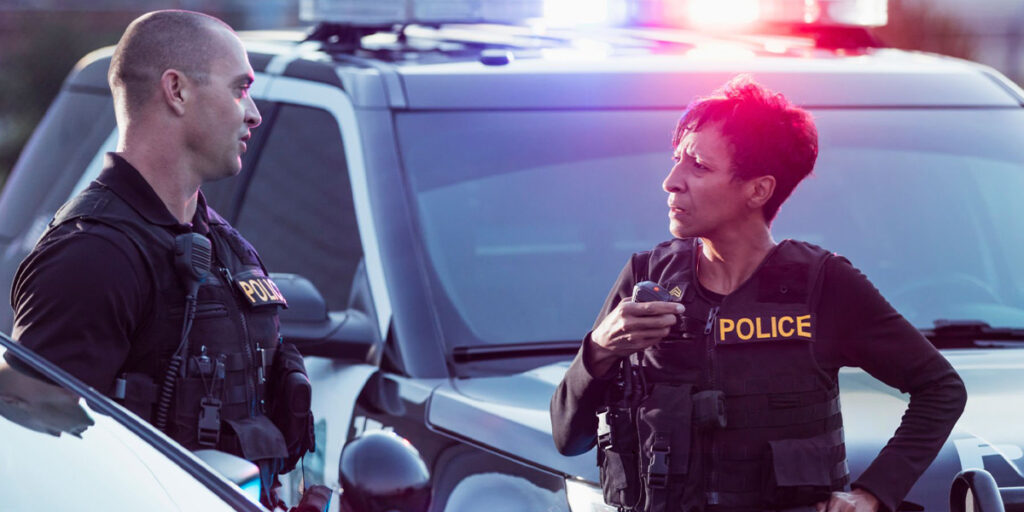
Access is time-bound, auditable, and limited to curated content. Infrastructure remains protected while intelligence moves efficiently to the appropriate stakeholders. For dispatchers and responding officers, verified visual context supports more accurate prioritization and safer response planning. Internally, security teams can coordinate investigations and escalations with greater clarity and speed.
A stronger response does not require broader system access. It requires disciplined control over how intelligence is delivered. By providing only verified, incident-specific intelligence, enterprise security teams can maintain organizational control while supporting collaboration with law enforcement.
Expanding Value Beyond Emergency Response
Controlled intelligence sharing should not be limited to high-risk incidents. Large enterprises can apply the same governance framework across security, compliance, and operational scenarios, including non-security incidents that require rapid video retrieval and internal distribution.
Event-based sharing can support:
- Internal investigations
- Workplace safety incidents
- Fraud review and compliance documentation
By using a consistent method across both internal and external scenarios, organizations increase system utilization without increasing exposure. Instead of creating separate processes for each situation, enterprises operate within a unified, auditable model. This consistency improves coordination, reduces operational friction, and strengthens measurable return on investment.
Conclusion
Organizations with established governance and risk management policies should not have to choose between protecting their systems and supporting an effective enterprise crime response. DirectToDispatch™ demonstrates that a governed, event-based intelligence-sharing model can strengthen collaboration without expanding risk.
Prioritizing control, time-bound access, and auditability, enterprises can improve situational awareness while preserving compliance and operational autonomy.
Read The Power of Curated Control white paper to explore the full framework behind controlled intelligence sharing.
FAQ
What is controlled intelligence sharing?
Controlled intelligence sharing is the practice of sharing verified, incident-specific intelligence through a governed, event-based process. Organizations determine what information is shared, who receives it, and how long access remains available, helping maintain organizational control while supporting law enforcement response.
Why is persistent access to security systems a concern?
Persistent access can increase cybersecurity, privacy, and governance responsibilities by extending visibility into enterprise systems. A controlled intelligence-sharing approach enables organizations to support verified incidents without granting ongoing access to internal security infrastructure.
How can enterprise security teams support law enforcement while maintaining organizational control?
Enterprise security teams can support law enforcement by sharing verified, incident-specific intelligence rather than providing direct access to internal systems. This approach helps preserve organizational control while giving dispatchers and responding officers relevant situational awareness during verified incidents.
How does controlled intelligence sharing improve incident response?
Controlled intelligence sharing provides dispatch-ready intelligence that helps support informed decision-making during verified incidents. By delivering relevant visual context while maintaining governance and organizational control, enterprises can strengthen collaboration with law enforcement without expanding system exposure.

 Joseph Courtesis
 Jason Lockett
 Ben Tucker